How GitHub Dependabot Works: From an Update Job to a Pull Request
Dependabot runs jobs: an isolated updater parses manifests, matches advisories by version, then asks a private API to open the pull request.
2026, Nov 05 — 24 minute read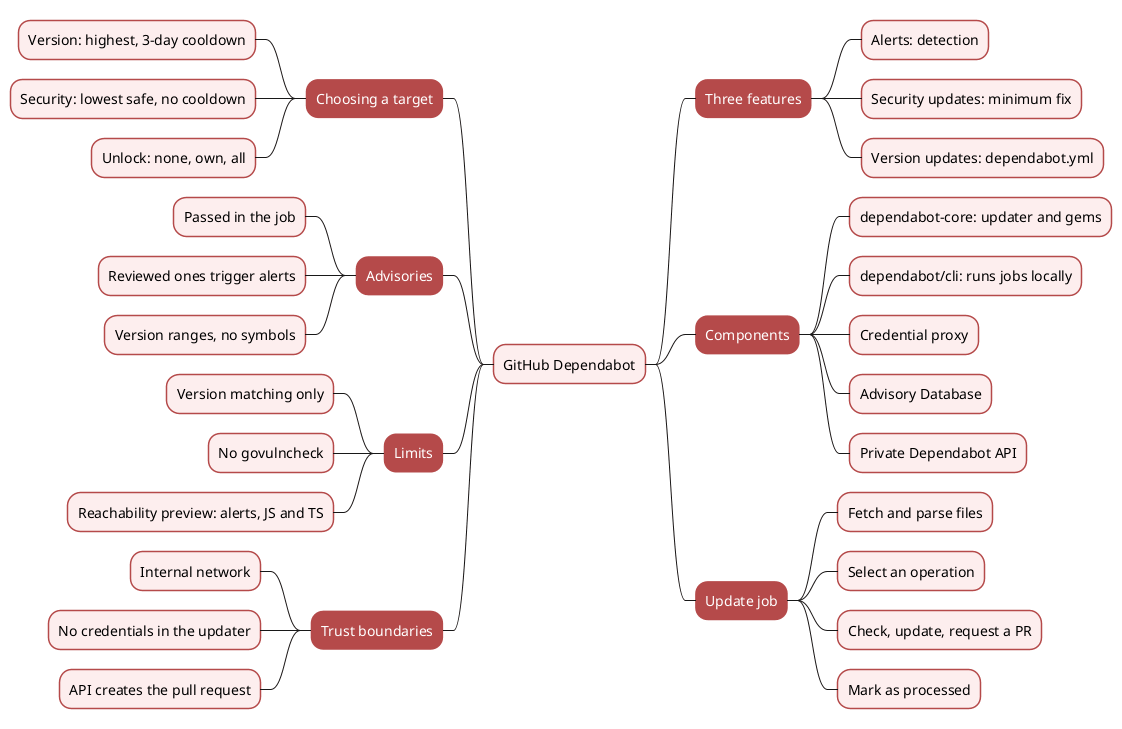
Dependabot runs jobs: an isolated updater parses manifests, matches advisories by version, then asks a private API to open the pull request.
2026, Nov 05 — 24 minute read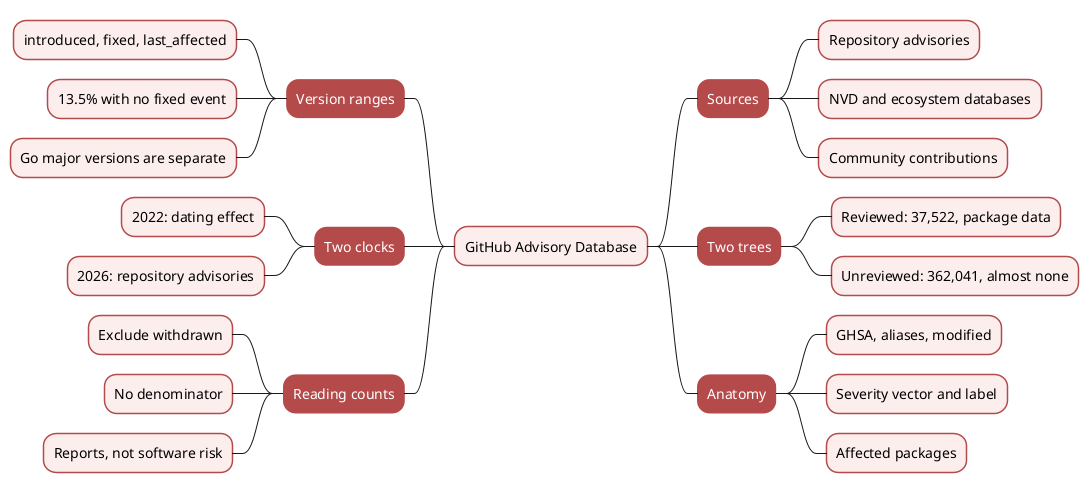
What the GitHub Advisory Database records, how to read OSV ranges, and why its yearly counts are not a trend: 36,266 reviewed advisories analysed.
2026, Nov 05 — 16 minute read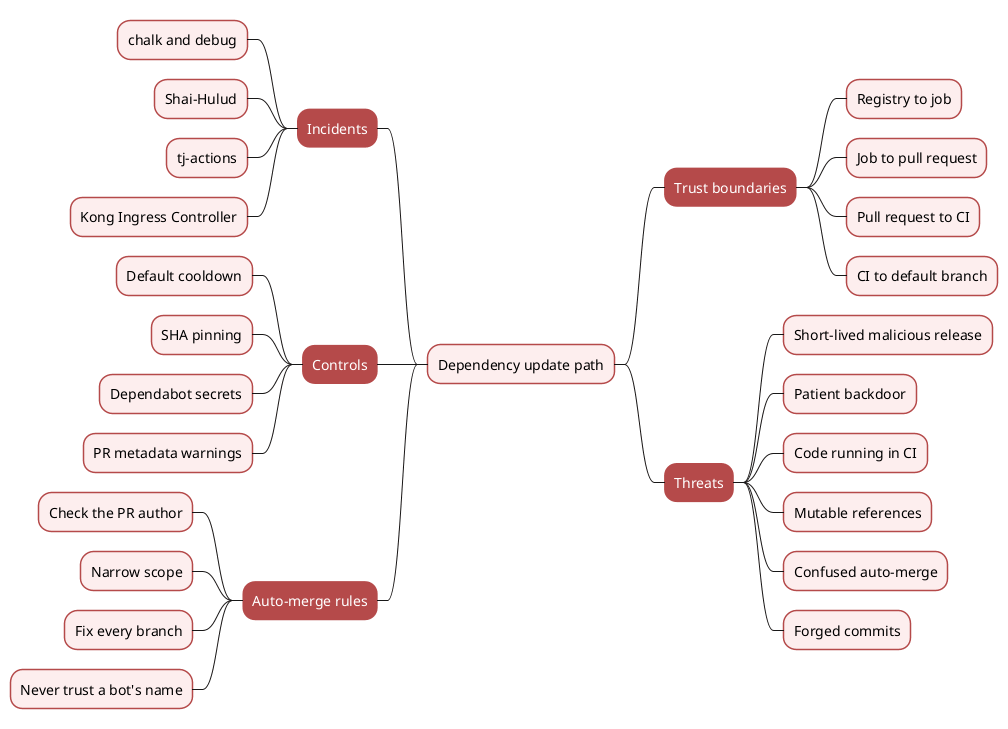
A threat model of automated dependency updates, using public incidents to show what cooldowns, read-only tokens and review stop, and what they miss.
2026, Nov 05 — 18 minute read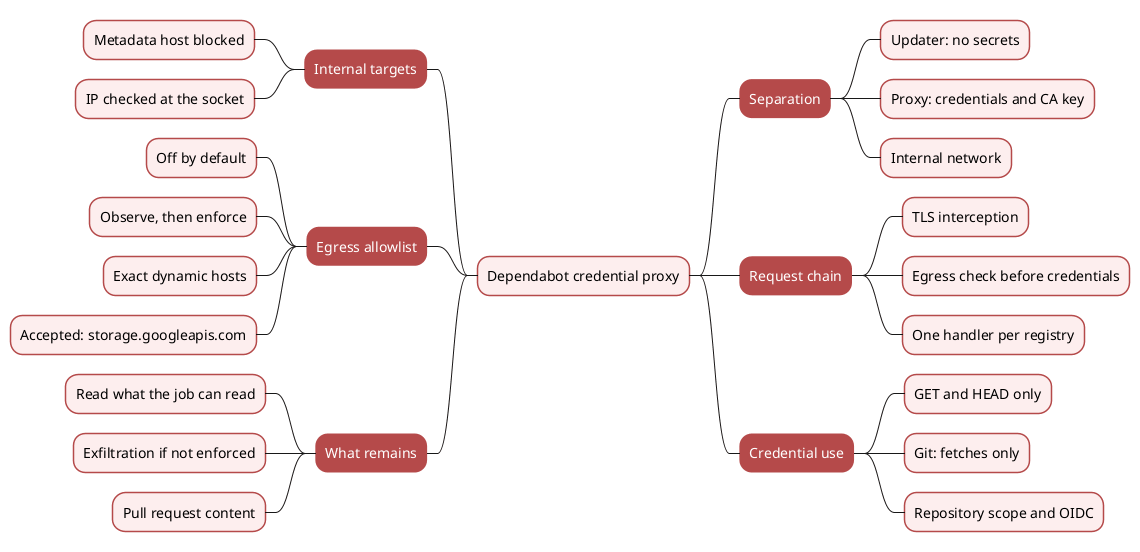
Dependabot's proxy adds credentials only to read requests. Its source shows what isolation stops, and why egress filtering is off by default.
2026, Nov 05 — 17 minute read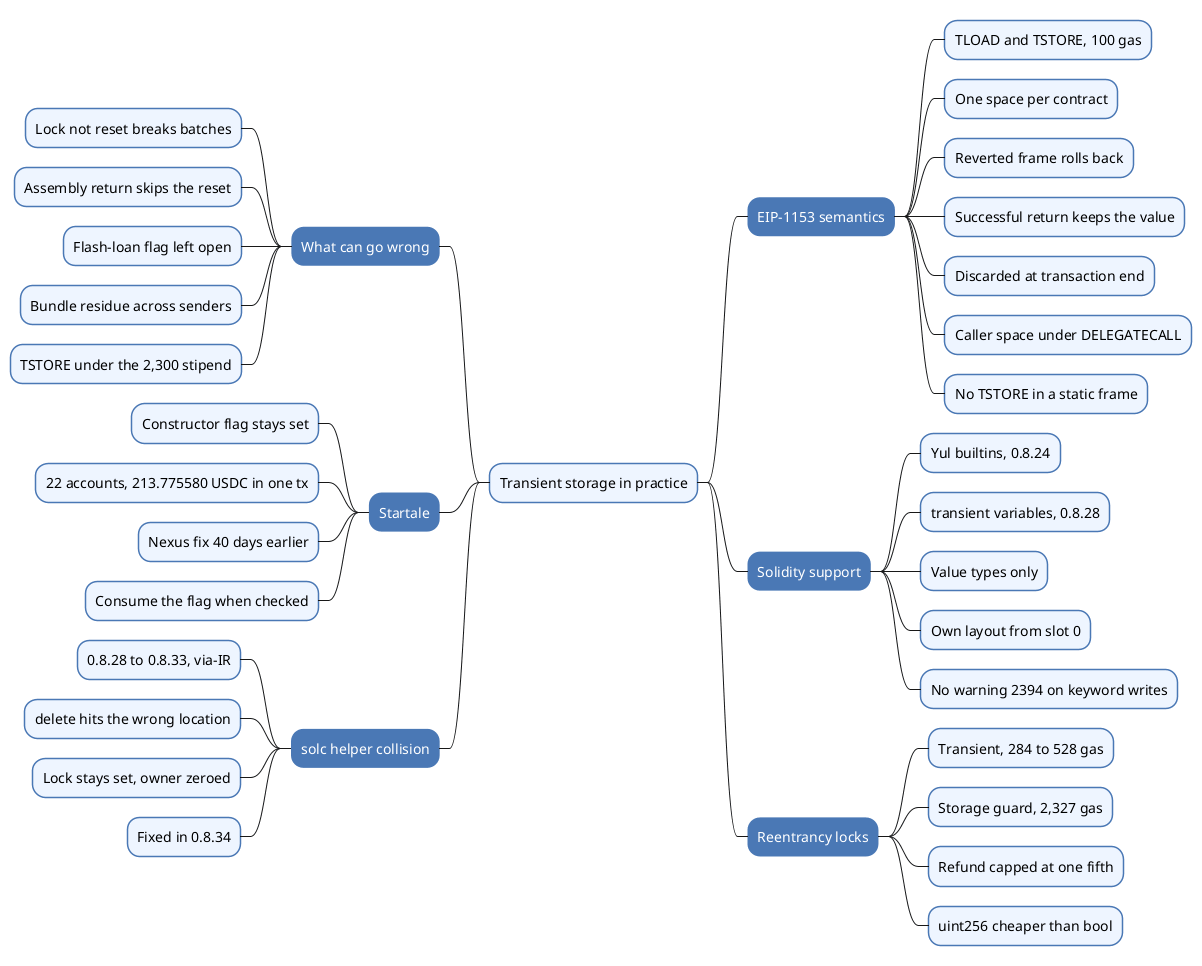
EIP-1153 from the spec to solc: measured lock gas, flags that outlive a call, the Startale drain and a solc via-IR bug, all reproduced with code.
2026, Nov 04 — 29 minute read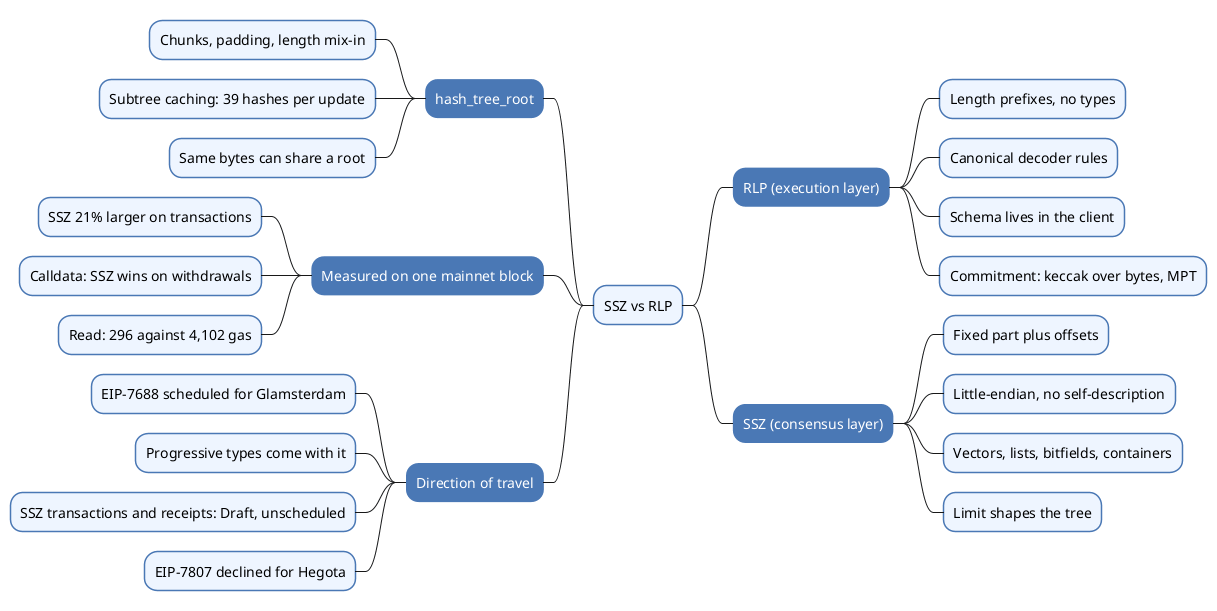
RLP and SSZ compared byte by byte on a real mainnet block: decoder strictness, hash_tree_root, sizes, Solidity gas, and what is scheduled.
2026, Nov 04 — 28 minute read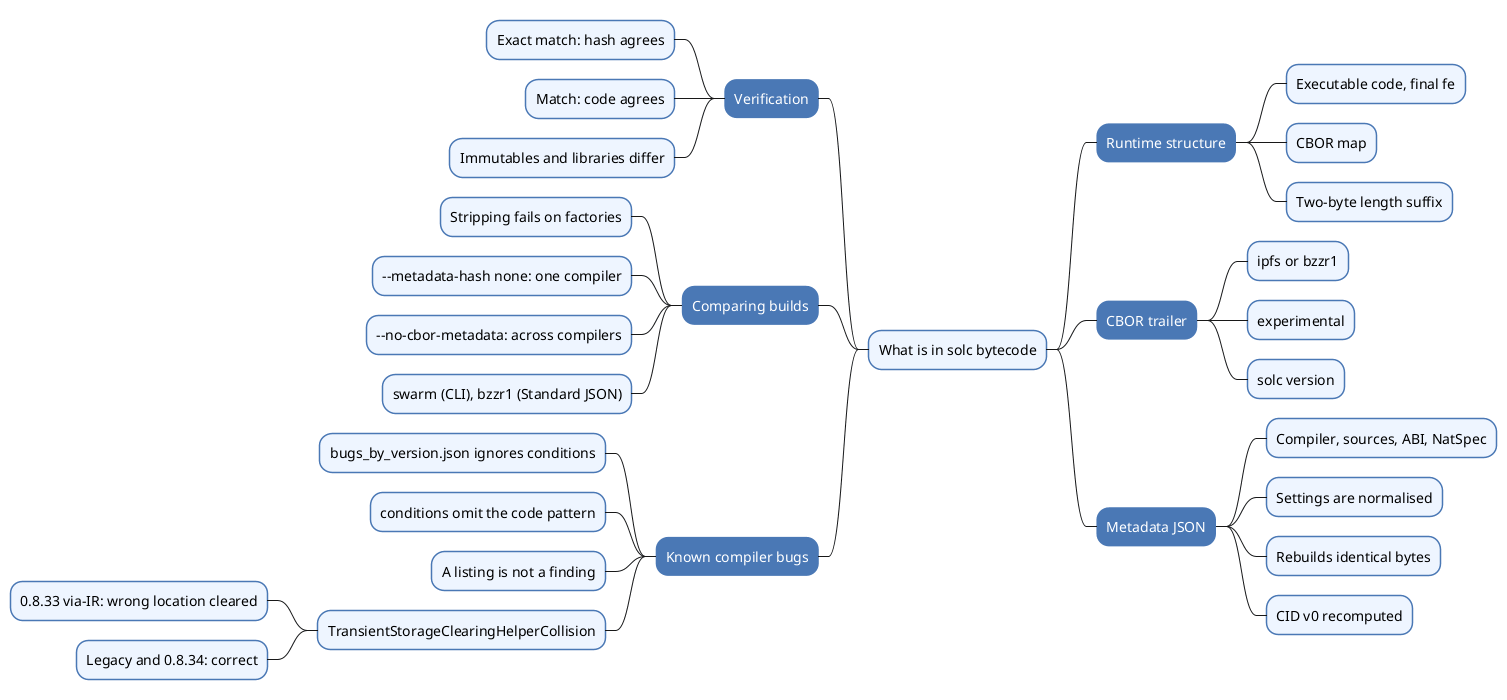
Decode solc's CBOR trailer, recompute its IPFS CID, compare factory builds reliably and test a known compiler bug, with outputs from real runs.
2026, Nov 04 — 34 minute read